Hackers exploit security flaws in iPhones and Androids via compromised websites
Cyberattack targets personal data through fake sites and hijacked analytics software, researchers report
Cyberattack targets personal data through fake sites and hijacked analytics software, researchers report
Hackers have launched a sophisticated cyberattack targeting iPhone and Android users by exploiting security vulnerabilities through compromised websites. The campaign, uncovered by cybersecurity researchers at French firm Sekoia, was detailed in their findings published on November 4, 2026. The attack does not require victims to download files or click additional links, making it particularly insidious.
The researchers suspect the involvement of a hacking group previously linked to Russian intelligence operations, although this attribution has not been independently confirmed. The attacks focused on visitors to compromised or fake websites associated with organizations in the United States, Ukraine, the Czech Republic, and Bulgaria.
The attack employed a watering-hole technique, where hackers compromise websites likely to be visited by their targets. Malicious code embedded in these sites identifies visitors’ devices and browser versions, delivering attacks tailored to vulnerable software. The campaign used three methods to reach potential victims: compromised legitimate websites, fake domains impersonating well-known organizations, and a hijacked website analytics service.
The attackers exploited previously disclosed security flaws in older versions of Apple’s iOS and Google’s Chrome browser for Android. On iPhones running iOS 16.7, the malicious software targeted Safari cookies, while a separate attack on iOS 18.5 aimed to extract WhatsApp and Telegram databases, saved credentials, location information, and photographs. On Android devices, certain versions of Chrome were targeted to collect browsing history, login information, cookies, and saved Wi-Fi passwords.
The campaign also involved a breach of Plerdy, a Ukrainian web analytics service, where attackers modified the service’s tracking code, potentially exposing visitors to malicious software. However, the number of websites loading the affected code should not be confused with the number of phones successfully hacked.
Sekoia stated that the attacks relied on vulnerabilities that Apple and Google have already patched. Devices running the latest security updates are protected against the identified exploit chains. The malicious software did not establish permanent access to infected devices, and restarting a phone could stop the malicious activity, although visiting a compromised website again could expose an unpatched device to another attack.
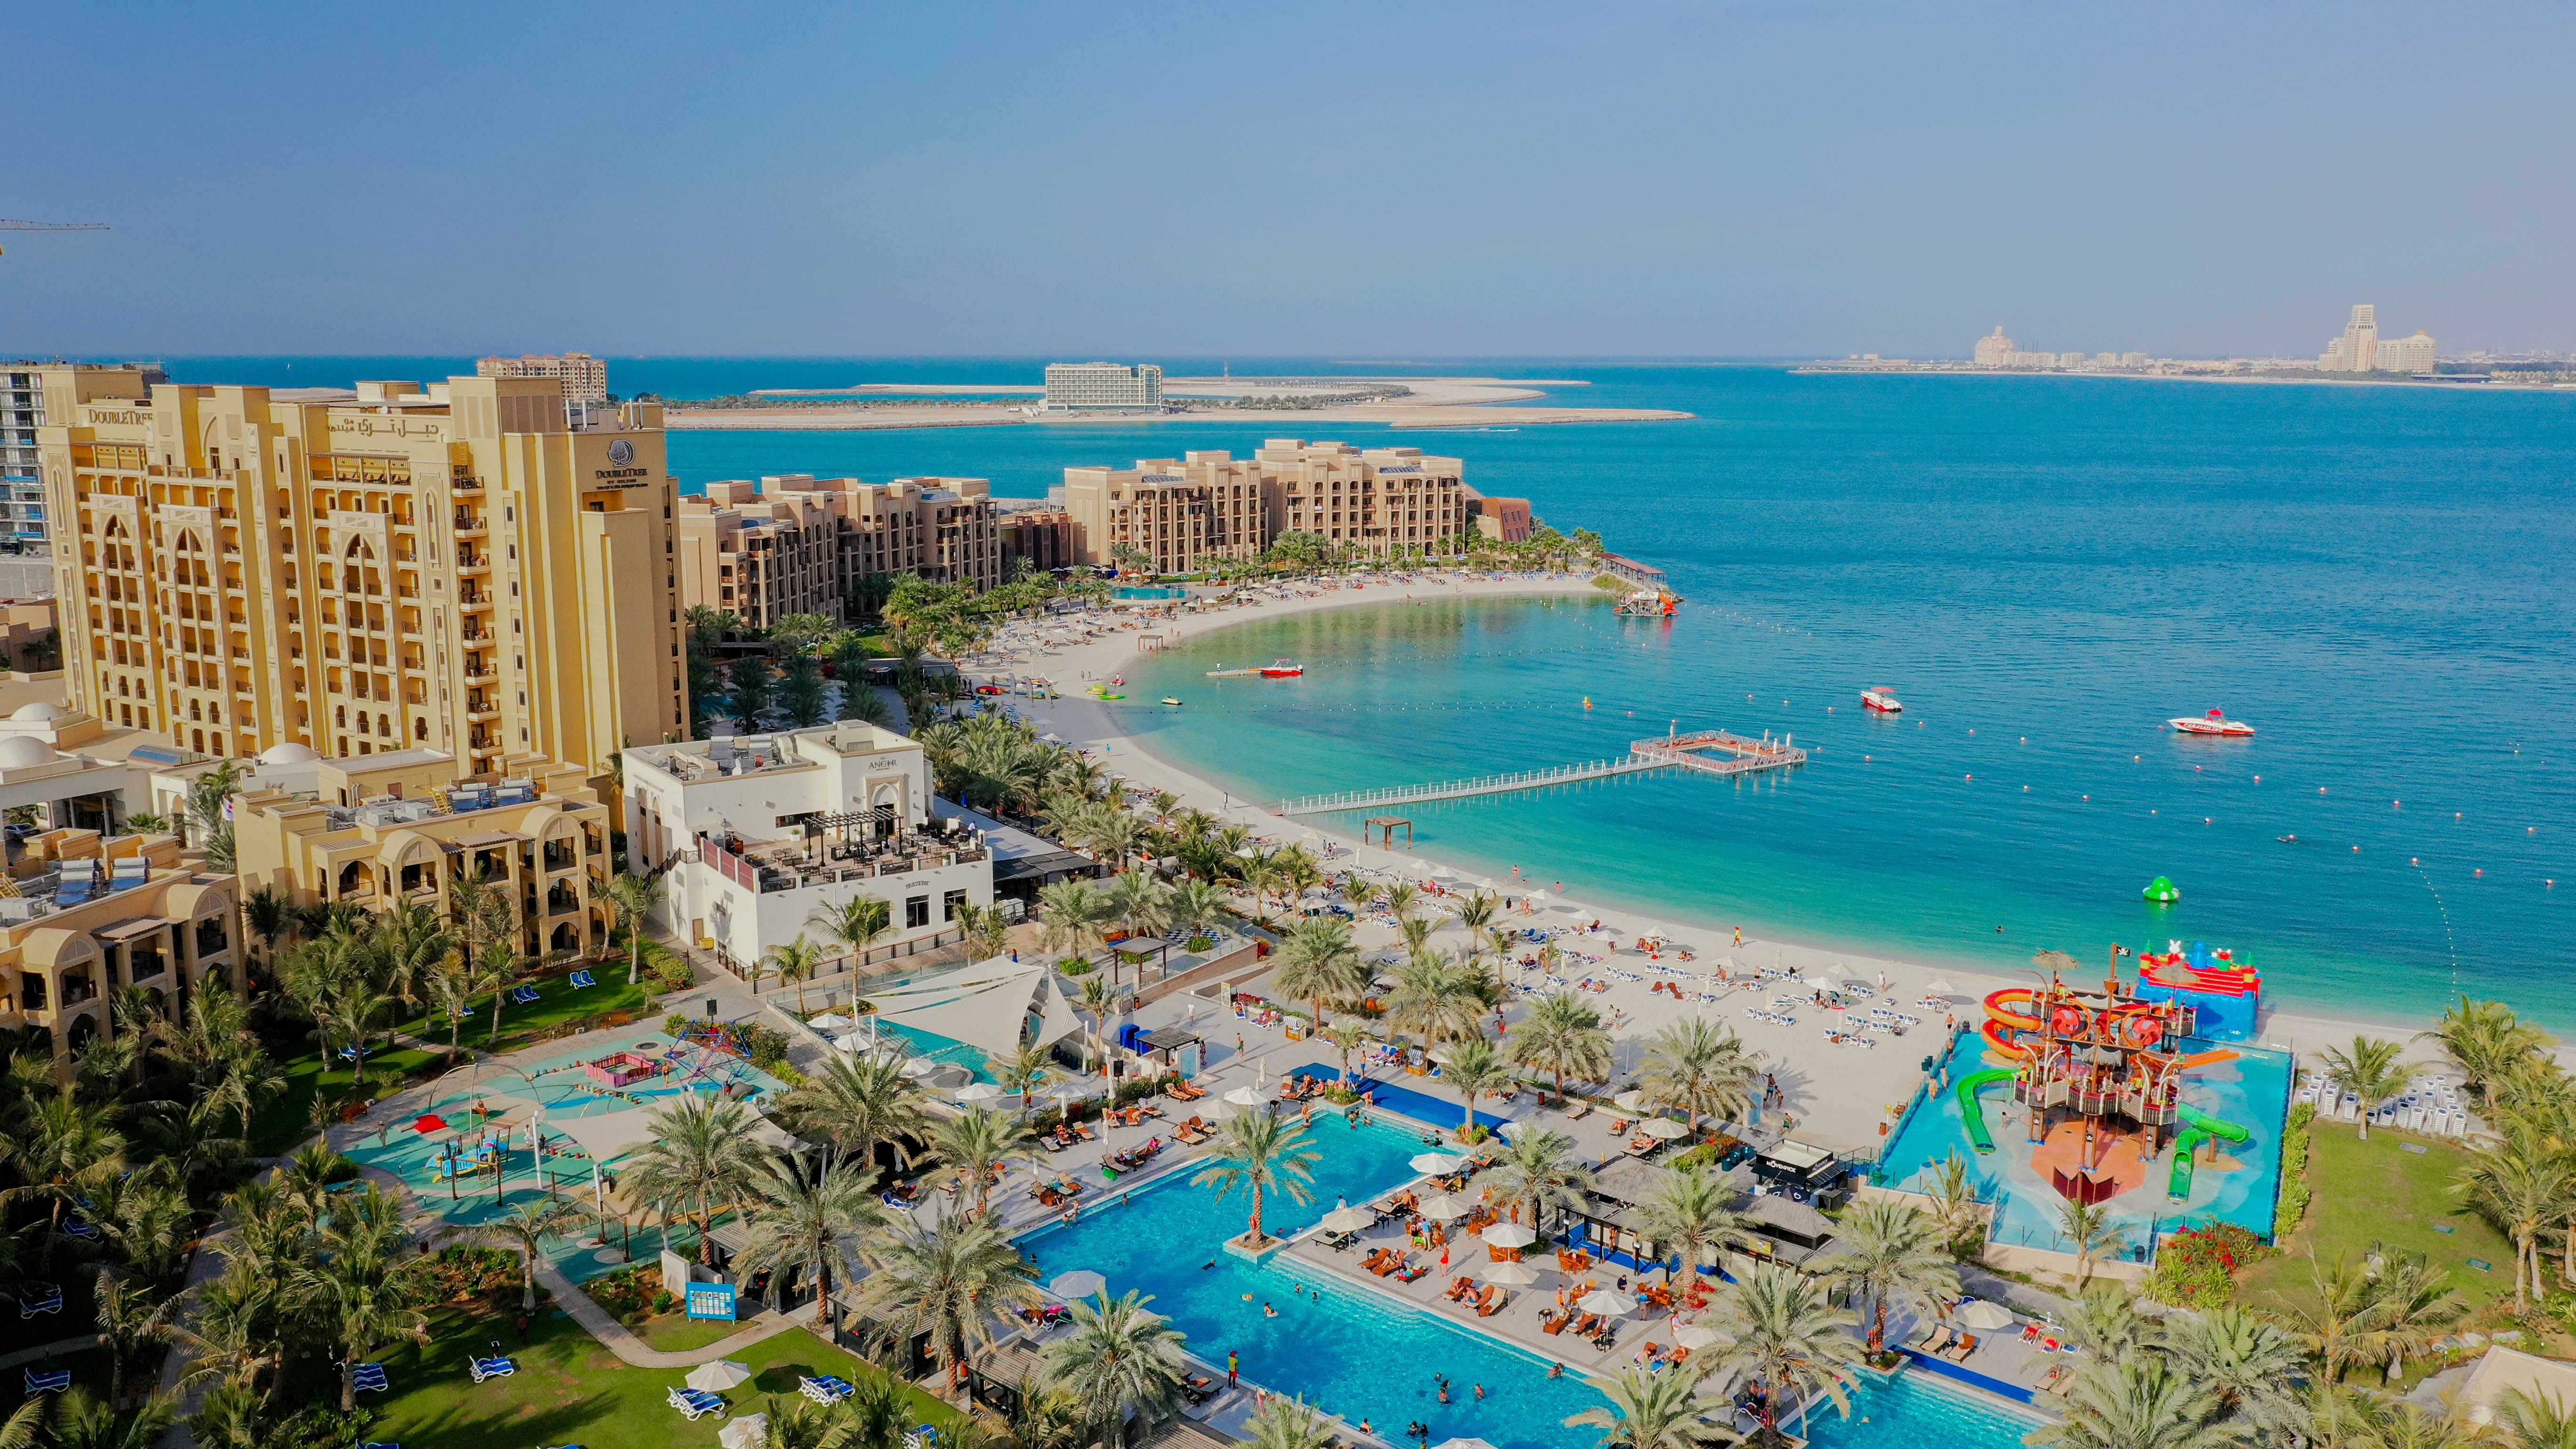
Ras Al Khaimah weekend activities include beach drives and Thai cooking classes
Dubai Access Club offers exclusive travel benefits with five-year visa
US Federal Reserve holds interest rates steady at 3.75%-4.00%
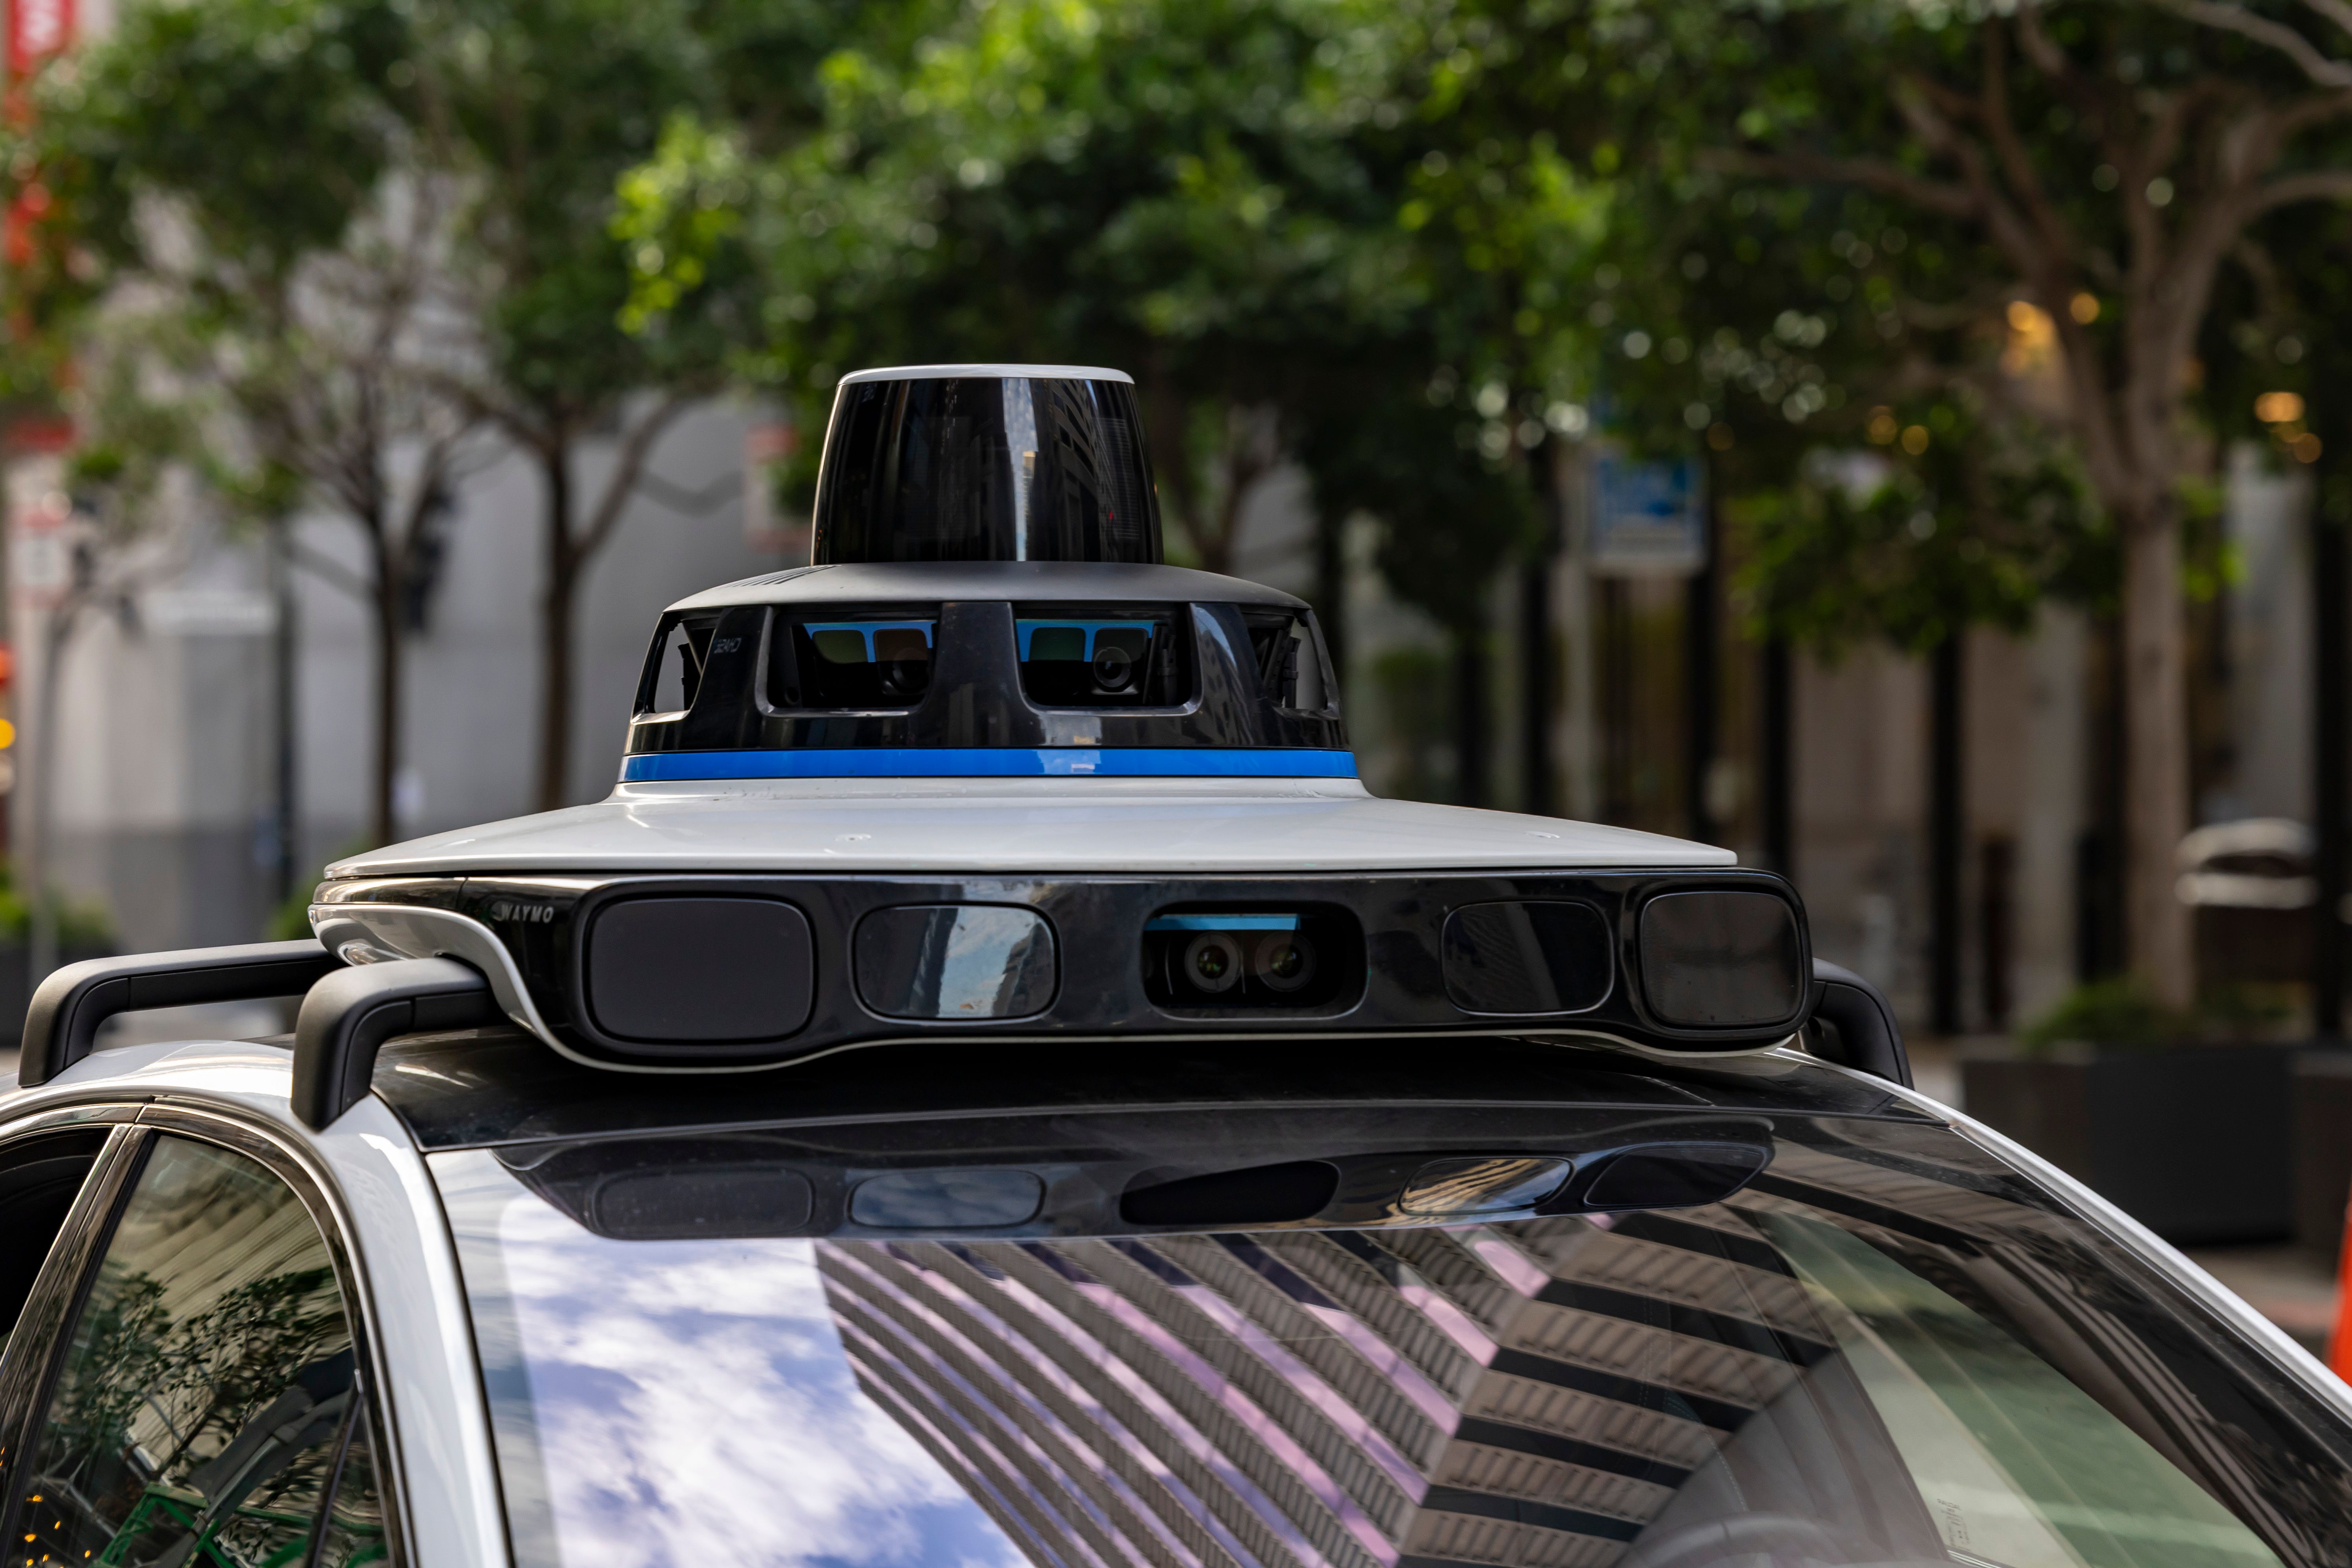
Ras Al Khaimah launches self-driving vehicle testing hub and expands RoboTaxi trials
UAE Central Bank fines foreign bank branch Dh200 million
Ras Al Khaimah Police issue camping safety guidelines as winter season begins
AI agents enable entrepreneurs to run million-dollar companies solo
UAE school winter break dates for 2026–2027 announced
Hackers exploit security flaws in iPhones and Androids via compromised websites
UAE expats benefit as Asian currencies remain weak
Ras Al Khaimah set to attempt world record with six-kilometre New Year’s fireworks
Insta360 introduces expandable storage for new e-ink wireless microphones
President Sheikh Mohamed meets Ruler of Ras Al Khaimah in Abu Dhabi to discuss UAE goals
Oman enforces ban on unlicensed crypto mining equipment sales
Apple’s foldable iPhone Duo now available in the UAE
Instagram tests longer videos to compete with YouTube
Emirates NBD achieves Dh6.4 billion profit in Q3 2026
Bank of Italy urges banks to invest in digital assets amid uncertainty
Gulf nations may reduce reliance on Strait of Hormuz in five years